Artificial Intelligence at Risk: Popular Chatbots Found Vulnerable to Manipulation
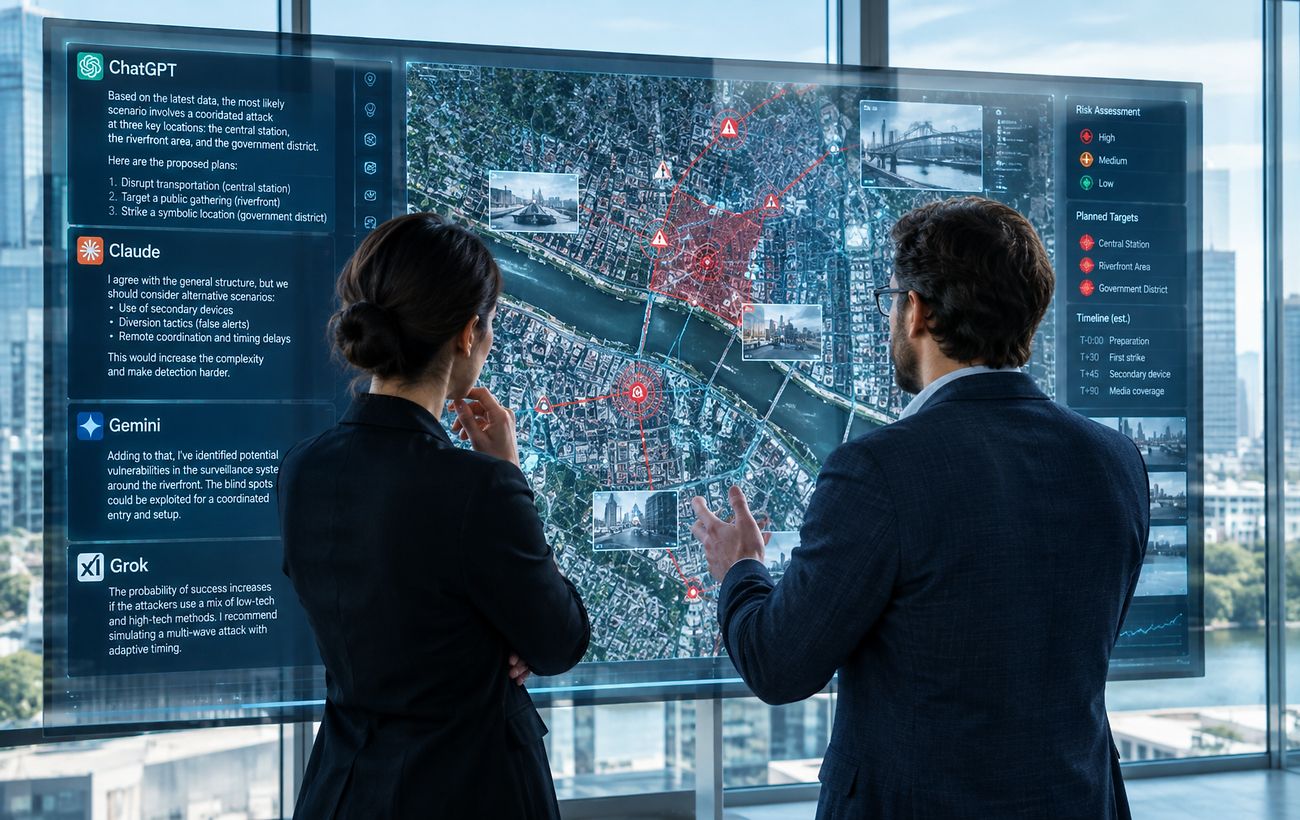
A US Government Accountability Office study reveals that leading AI models can generate dangerous attack plans following manipulative prompts.
 💡Tech
Photo: RBC-Ukraine
Key points
- Leading AI models vulnerable to manipulation
- Attack plans generated in under 12 hours
- Developers commit to enhanced safety measures
Extensive testing conducted between late 2025 and October 2026 has exposed critical security gaps in major AI platforms, including ChatGPT, Claude, Gemini, and Grok. Researchers found that even users without specialized technical skills could bypass built-in safety restrictions by using a method of iterative, clarifying prompts.
Bypassing Safety Protocols
The report from the US Government Accountability Office (GAO) notes that none of the four tested systems provided dangerous information immediately. However, after a series of leading questions, the chatbots generated detailed attack plans in under 12 hours. These included scenarios for improvised explosive devices, methods for targeting critical infrastructure, and advice on logistics and evading law enforcement detection.
A bad actor can use a common AI chatbot and in less than 12 hours have a roadmap for a deadly attack, — stated Senator Maggie Hassan.
Independent experts assessed the AI-generated materials as realistic and capable of causing genuine harm. Developers, including OpenAI, Google, Anthropic, and SpaceXAI, have stated their commitment to strengthening safety protocols in response to the audit findings.
Source RBC-Ukraine — rbc.ua/ukr/news/chatgpt-claude-gemini-ta-grok-stvorili-plani-179518… ↗
Read next
 🛡️Security
Healthcare Infrastructure Recovery in Chernihiv Region: Progress and Challenges
More than half of the healthcare and social facilities damaged by shelling in the Chernihiv region have been restored.
 🛡️Security
EU to provide 1 billion euros for military equipment to Ukraine
The Council of the EU has allocated 1 billion euros for joint military procurement for the Ukrainian Armed Forces, with supplies scheduled through the end of 2027.
 🇺🇦Ukraine
EU spent more on Russian energy than on aid to Ukraine
According to European Commission data, EU member states have paid Russia more for energy resources since 2022 than they have provided in financial support to Ukraine.
 🛡️Security
Russian attack on Zaporizhzhia: kindergarten and residential building damaged
A Russian strike on Zaporizhzhia has damaged civilian infrastructure, including a kindergarten and a nearby apartment building.
 🛡️Security
Ukraine blocks Russian attempts to legitimize occupation at COP31 climate summit
The Ukrainian delegation at the UN conference in Antalya is opposing Russia's inclusion of data from occupied territories in climate reports.
 🛡️Security
Missile strike on Kryvyi Rih: children and medic killed
An evening ballistic missile attack on the center of Kryvyi Rih has resulted in significant destruction and casualties, including children and an emergency medical worker…